


Prevent Key Loss and Audit Failures for US Home Care Call Recordings

Treat every recorded call as a sensitive data asset, not a convenience feature. That means requiring AES-256 encryption in transit and at rest, customer-controlled key management instead of a vendor’s default keys, role-based access with immutable audit logs, automated consent announcements, and a written retention and disposal schedule. This baseline protects protected health information (PHI) discussed during intake and care calls, and it gives you a paper trail the moment a state auditor or a family’s attorney asks who listened to a recording and why. Before signing with any vendor, ask them to show you the key management console, not just the sales deck.
TL;DR:
Home care agencies must require encryption of call recordings both during transit and at rest, with AES-256 and customer-managed keys for maximum security.
Protecting PHI in recordings mandates strict access controls, immutable audit logs, and live masking of sensitive payment data to prevent leaks and ensure compliance.
Agencies should verify vendor practices, including key rotation schedules and automatic DTMF masking, before signing contracts to avoid audit and breach risks.
State laws on recording consent vary, so it is safest to automate consent notices in every call and log consent events alongside the recordings.
Building secure recording practices into daily operations requires policies, staff training, regular testing, and using managed services for automation and compliance consistency.
Table of Contents
What Secure Call Recordings Mean for a Home Care Agency
A “secure” recording is not just a password-protected file. It requires two distinct layers of protection: encryption in transit, which scrambles the audio while it travels from the caller’s phone to your storage, and encryption at rest, which protects the file once it’s sitting in a database or cloud bucket. Industry guidance from the NIST Cybersecurity Framework points to AES-256 as the standard cipher for stored audio, and most serious platforms now build on it by default.
For home care agencies, the harder question is scope. A recorded call between an intake coordinator and a prospective client’s family almost always touches PHI, medication names, diagnoses, care schedules, which pulls that recording under HIPAA’s Security Rule. A cold sales call from a marketing vendor usually does not.
Layer on top of that the patchwork of state consent laws. Some states allow recording with only one party’s knowledge; others require every participant to consent. The lifecycle that ties all of this together looks like:
Capture: record only the calls that need it, on the extensions that need it.
Protect: encrypt immediately, never store plaintext audio.
Control access: limit who can play back or export a file.
Retain: keep recordings only as long as policy and law require.
Dispose: destroy files securely when the retention window closes.
Essential Technical Controls to Require From Any Vendor
Before you sign a contract with any call platform, run the vendor through a short list of non-negotiable technical requirements. Skipping this step is how agencies end up with recordings they can’t produce during an audit, or worse, a breach they can’t explain.
Encryption everywhere it counts. Require server-side encryption using KMS-backed keys (SSE-KMS or equivalent) for stored files, plus TLS or DTLS-SRTP for the media stream itself.
Customer-managed keys. Ask whether the platform supports bring-your-own-key (BYOK) or customer-managed key (CMK) arrangements, with clear rotation schedules, revocation procedures, and hardware security module (HSM) backing for the highest-sensitivity accounts.
Role-based access control with immutable logs. Every playback, download, or export should generate a log entry that nobody, including administrators, can quietly delete.
Real-time masking for payment data. DTMF masking strips payment card digits from the audio stream before they’re ever recorded, which keeps card numbers out of storage entirely, a stronger safeguard than pausing and resuming the recording manually according to Paytia’s PCI-compliant recording guidance.
Locked-down storage configuration. Confirm private buckets, versioning, and enforced SSL connections. A public or misconfigured storage bucket is one of the most common ways healthcare recordings leak.
Pro Tip: Ask your vendor for a screenshot of their key rotation schedule during the sales call. If they can’t produce one immediately, they probably don’t have a real one.
HIPAA and State Consent Rules Home Care Agencies Must Know
Two separate legal frameworks govern your recordings, and confusing them is where most agencies get into trouble. HIPAA governs what happens once a recording contains PHI. The HIPAA Security Rule requires administrative, physical, and technical safeguards, meaning access controls, audit logs, and a documented “minimum necessary” policy for who can hear a given call.
State consent law governs whether you can record the call at all. A handful of states require all parties to consent before a call is recorded; most allow recording with the knowledge of just one party. Because home care agencies field calls from families and caregivers across state lines, the safest posture is to assume all-party consent applies and automate a spoken notice at the start of every recorded call.
Documentation matters as much as the technology:
Keep the exact script your automated system reads at the start of each call.
Maintain a written consent policy that names who can request playback and under what circumstances.
Log consent events alongside the recording itself, not in a separate spreadsheet nobody checks.
Building Secure Recordings Into Daily Operations
Technology alone doesn’t make recordings secure. Staff habits and vendor configuration decide whether the controls you paid for actually work day to day.
Write the policy first. Classify call types, set a retention window for each class (intake calls, care coordination, billing disputes), and define a legal-hold process for calls under dispute.
Automate what you can. Configure the system to play consent announcements automatically, record only the queues that need it, and mask DTMF tones during payment discussions.
Lock down access and stream the logs. Set RBAC by job role, restrict who can export files, and route audit logs into a SIEM or a secure archive rather than leaving them sitting in the call platform’s default dashboard.
Train staff and plan for failure. Every employee who touches recordings needs basic training on what they can access and why, and your IT contact or managed provider needs a documented key-loss recovery plan, including a backup HSM or KMS path.
Verify it actually works. Periodically test that encrypted files still decrypt, sample a handful of recordings for playback accuracy, and rehearse key rotation before you need it in an emergency.
Pro Tip: Run a full decrypt test on a non-production account every quarter. Finding out your recovery key doesn’t work during an actual audit is the worst possible time to learn that.
How Leading Platforms Implement Secure Recording Encryption
Two implementation patterns show up repeatedly in real-world deployments, and both are worth understanding even if you’re working through a managed provider rather than building this yourself.
Amazon Connect, paired with S3 storage, supports customer-managed KMS keys for recordings, transcripts, and analytics output. That setup lets an agency’s IT team define key policies, grant specific permissions to specific roles, and pull a full CloudTrail audit history of every key operation, who rotated it, who accessed it, when.
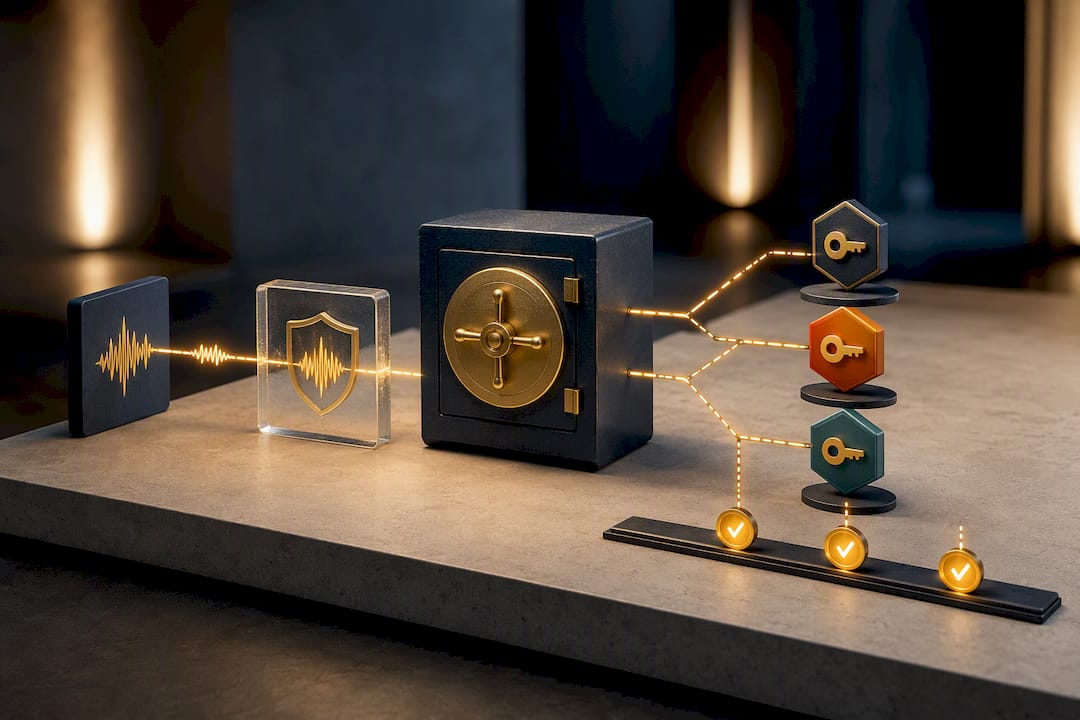
Twilio takes a different approach with hybrid encryption: each recording gets encrypted with a unique AES-256 content key, and that key is then wrapped with the customer’s own RSA public key. Only the holder of the matching private key can ever decrypt the file, per Twilio’s own documentation. That’s powerful for tenant-only control, but it comes with a real trade-off: lose the private key, and the recordings become permanently unreadable, even to Twilio.
Whichever pattern your provider uses, insist on:
Cross-region replication with separate CMKs for disaster recovery, not a single point of failure.
Full end-to-end decrypt testing on a non-production account before rolling changes into live systems.
DTMF masking and transcript redaction running automatically, not as a manual step someone forgets during a busy shift.
How The BOSS System Handles Secure Call Recording in Practice
Running a home care agency taught me that secure recording only works when it’s automated into the workflow, not left to whoever answers the phone at 2 AM. A managed command center can build consent announcements, restricted playback access, and documentation directly into after-hours calls. This approach can help reduce missed calls, improve record accuracy when disputes arise, and lessen administrative work for agency owners.
— Ian Dwight Abejo
Let a Managed Command Center Handle the Compliance Burden
Building this yourself means someone on your team owns key rotation, RBAC configuration, consent scripting, and audit log monitoring, on top of everything else running your agency.
Beyond after-hours coverage, dedicated virtual assistants trained specifically in home care operations can manage intake calls, scheduling, and documentation using the same secure handling practices, without you having to vet a call platform’s encryption settings yourself. If you’re ready to see how a managed on-call program handles this for your agency, start with a free trial of the virtual assistant service and get a firsthand look at how the documentation and access controls work before you commit to anything.
Where to Verify These Standards Yourself
AWS re:Post KMS guide and Twilio’s encryption docs
HIPAA compliance primer for practices
Sources
FAQ
Do Home Care Agencies Need to Encrypt All Call Recordings?
Yes, any recording likely to contain PHI, which covers most intake, scheduling, and care coordination calls, needs AES-256 encryption at rest and in transit under HIPAA’s Security Rule safeguards.
Is One-Party Consent Enough for Recording Calls?
It depends on the state; some states permit recording with only one party’s knowledge, while others require all parties to consent, so agencies serving multiple states should default to automated consent announcements on every call.
What Happens if a Recording Encryption Key Is Lost?
With hybrid encryption models like Twilio’s, losing the private key makes the recording permanently unreadable, which is why a documented backup and multi-person key recovery process is essential.
Can a Managed Service Handle Secure Call Recording for Us?
Yes, A managed command center can build consent automation, restricted access, and documentation into after-hours call handling, removing the burden of configuring encryption and audit logging in-house.
How Long Should a Home Care Agency Keep Call Recordings?
Retention should follow a written policy tied to call type, care coordination calls tied to active clients typically need longer retention than routine scheduling calls, with secure disposal once the window closes.
Recommended


Comments